12 months of updates and support Support: Mon–Fri 10:00–18:00 Average response — under 2 hours
Telegram WhatsApp
Request a module
Items in your cart

Shopping cart

0

Your cart is empty

Add the modules you need and they will appear here.

PrestaShop Ready to install

CMS Security Scanner for PrestaShop

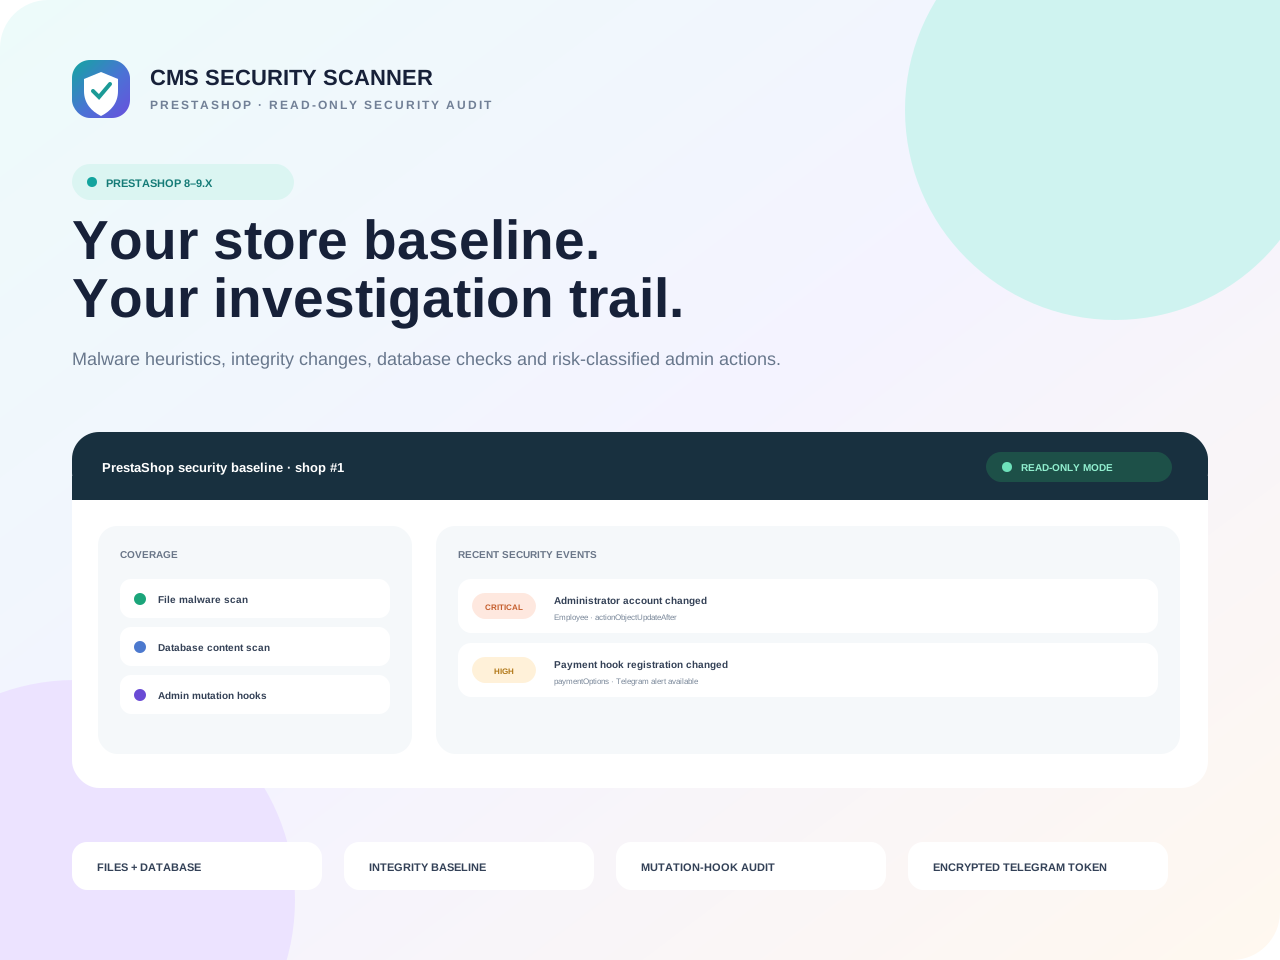
CMS Security Scanner gives a store owner a clear risk picture: malware-oriented file checks, new/changed/missing file detection, security-relevant database baselines and an audit trail of risky administrator actions.

PrestaShop 8.xPrestaShop 9.x
Limited-time offer Free module installation by our team

Select installation in the product options. After checkout, we will arrange access, install the module and run a basic check on your store.

The module licence is charged separately. Paid third-party services and non-standard development are not included.
0.00 грн. installation
2,490.00 грн. Ex Tax: 2,490.00 грн.
Updated24/08/2026

Files available after payment

No core file overwritesBack Office / ZIP
12 months of updatesUpdated 24/08/2026
Developer supportReady to install
Clean codeDocumented structure

CMS Security Scanner gives a store owner a clear risk picture: malware-oriented file checks, new/changed/missing file detection, security-relevant database baselines and an audit trail of risky administrator actions.

Notice a suspicious change before it becomes an incidentThe scanner is strictly read-only: it never deletes, quarantines or auto-fixes files and never hides findings. The administrator remains in control.
SEC
CMS Security ScannerREAD-ONLY INVESTIGATION DASHBOARD
SCAN COMPLETE
92integrity score1 HIGH · 3 MEDIUM · 8 INFO
18,420files checked
3baseline changes
146DB entities

Four security layers in one report

Filesystem, integrity baseline, database and administrative changes are reviewed together. Findings include severity and context for manual investigation.

FILESFile scanwebshell, eval/base64, hidden PHP and unsafe .htaccess
BASELINEIntegritynew, changed, missing and unverifiable files
DATABASEDatabaseadmins, permissions, modules, API, hooks and content
AUDITEventscritical changes and Telegram notifications

Malware heuristics

Webshell behaviour, obfuscation, encoded payloads, PHP in non-PHP files and known denylisted hashes.

Store-specific baseline

After manual review, remember current hashes and detect files that are new, modified or missing later.

Database controls

Employees, profiles, webservice accounts, modules, hook registrations and injected code in configuration or descriptions.

Administrator audit

Verified data-mutation hooks classify administrator, permission, API, module, configuration and payment-hook changes.

Telegram for high risk

High and critical findings can be pushed to Telegram without waiting for the next Back Office visit.

Investigation history retained

Uninstall disables integration while preserving reports, baselines and journal data for recovery or investigation.

A safe first-run sequence

InstallUpload the ZIP through the native module manager.
ScanRun the scanner and wait for the completed report.
Review manuallySeparate expected store changes from suspicious ones.
Create baselineRemember only a state you have already reviewed.

A scanner is not a substitute for incident response

A heuristic match is an investigation lead, not automatic proof of compromise. There is no CVE feed, official release-manifest comparison or php.ini remediation. Confirm a serious finding manually or escalate it to a specialist.

COMPATIBILITY

PrestaShop 8.x–9.x; PrestaShop 1.7 is not advertised

A native Back Office module with protected own tables and report directories. The Telegram token uses PrestaShop encryption and API keys are only shown in masked form.

Included with the purchase

Installation-ready ZIP, readable unencrypted source, read-only engine, file/database checks, baseline, audit journal, Telegram alerts, documentation, 12 months of updates and launch support.
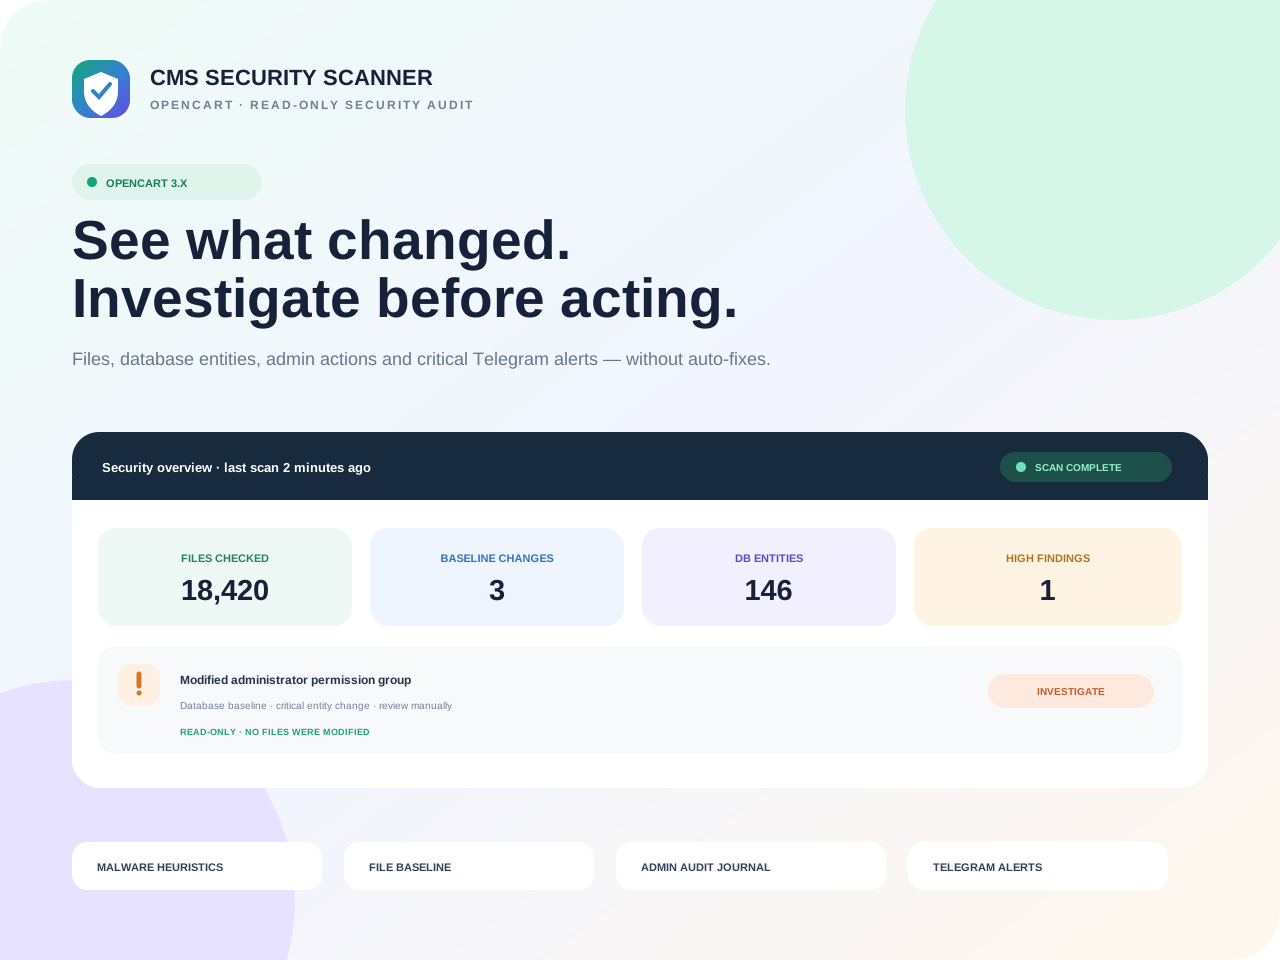
Need the OpenCart edition?A separate native edition accounts for the other platform’s files, tables and administrator events.
View the edition
BUILT FOR COMMERCE

Module features

Thoughtful functionality for a real store, without unnecessary complexity.

File scanning

Webshell behaviour, obfuscation, encoded payloads, hidden PHP and known dangerous hashes.

01

Integrity baseline

Detect new, modified, missing and unverifiable files relative to a reviewed baseline.

02

Database controls

Review administrators, permissions, modules, integrations and editable content for suspicious changes.

03

Administrator audit

Record administrator, permission, extension, configuration and payment-surface changes.

04

Telegram alerts

Push high and critical events to the responsible specialist immediately.

05

Strictly read-only

The module never deletes, quarantines or automatically remediates anything.

06
QUICK START

Review first, then create a trusted baseline

Never baseline blindly: inspect the first report and only remember the current state after manual validation.

01

Install the module

Upload the ZIP through Module Manager and open CMS Security Scanner in Back Office.

02

Run the scan

Wait for the complete report and manually review high, medium and informational findings.

03

Create the baseline

After confirming current files and entities are legitimate, remember the current state.

TECH DETAILS

Technical specifications

CMS Security Scanner gives a store owner a clear risk picture: malware-oriented file checks, new/changed/missing file detection, security-relevant database baselines and an audit trail of risky administrator actions.

Ready to installIn Stock
PlatformPrestaShop
Compatible versions8.x, 9.x
InstallationBack Office / ZIP
PHP versionPHP — per PrestaShop requirements
Licence1 domain
LocalisationУкраїнська, English, Русский
{ }

Need help or a custom change?

We can check compatibility, help with installation or adapt the module to your workflow.

Discuss the task
FAQ

Frequently asked questions

Developer support

Will the scanner delete an infected file?

No. This is deliberately read-only: it reports risk and context but never changes the store automatically.

Does every finding prove compromise?

No. Heuristics can match legitimate complex code. A serious result must be confirmed manually.

What survives uninstall?

Reports, baselines and audit history are deliberately retained so an investigation survives reinstall.

Does it include a CVE feed or automatic remediation?

No. It has no CVE feed, automatic quarantine or php.ini remediation. It is a detection and change-control tool.