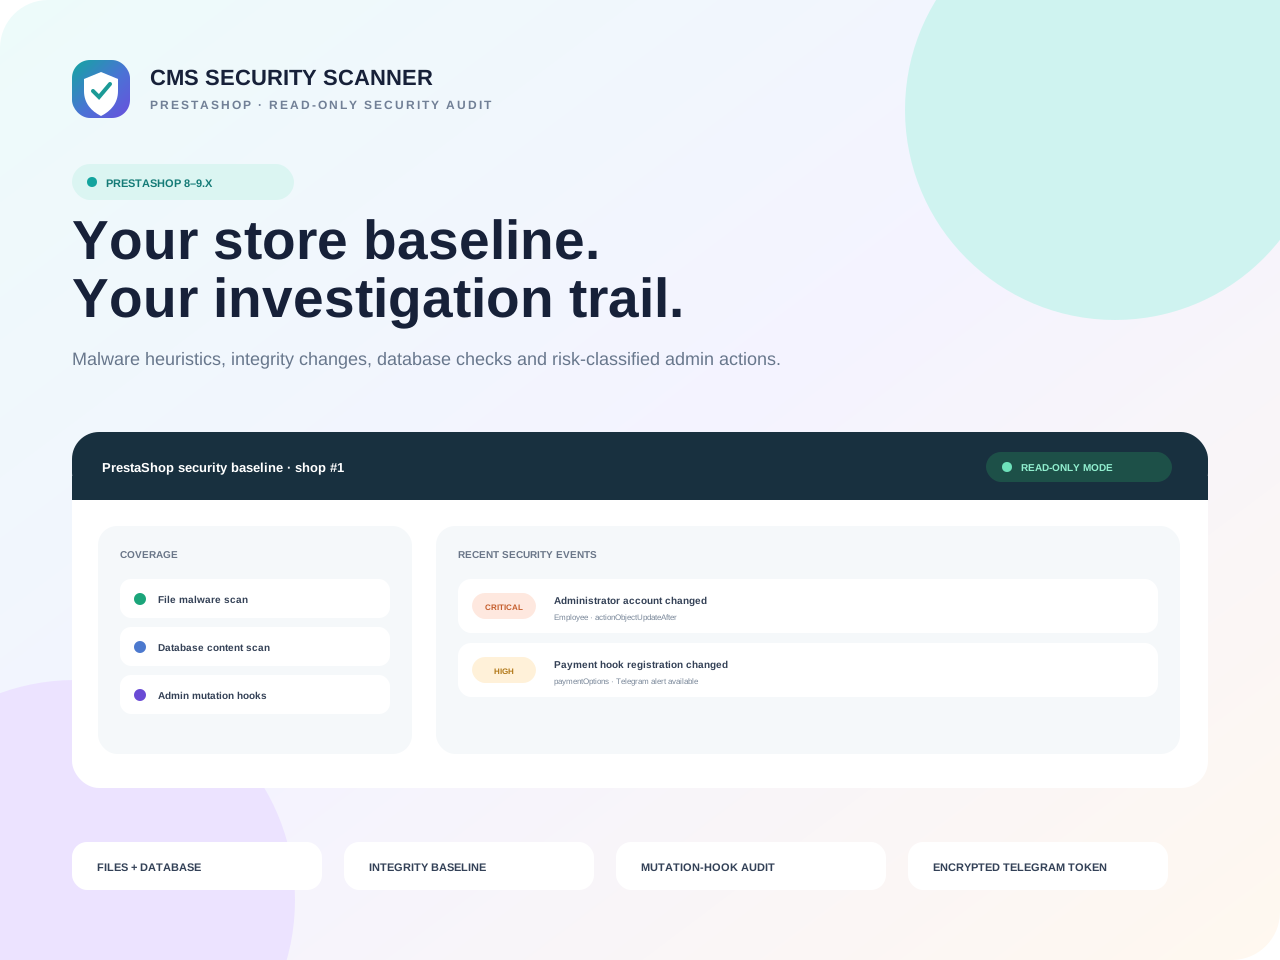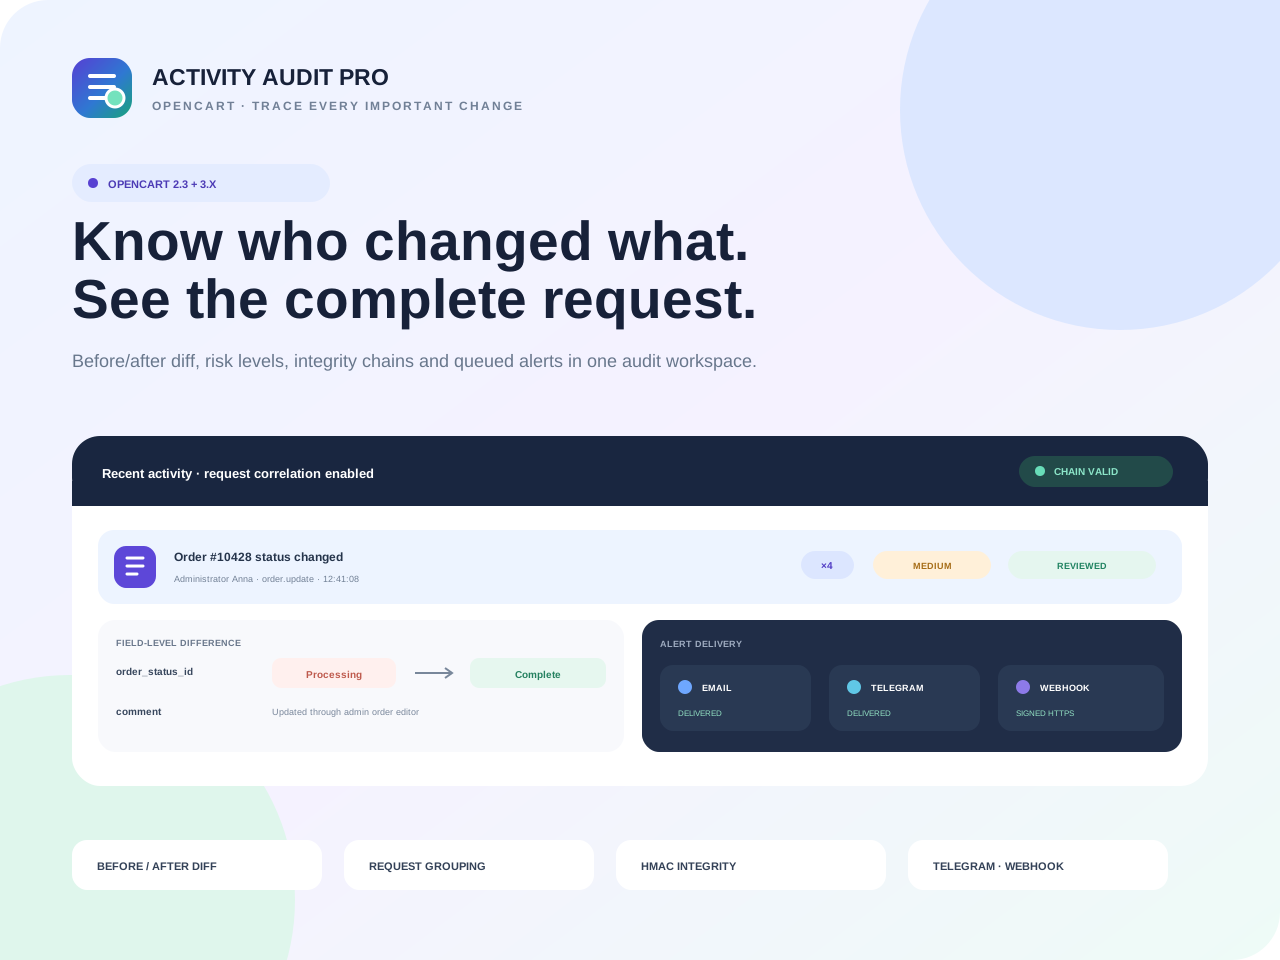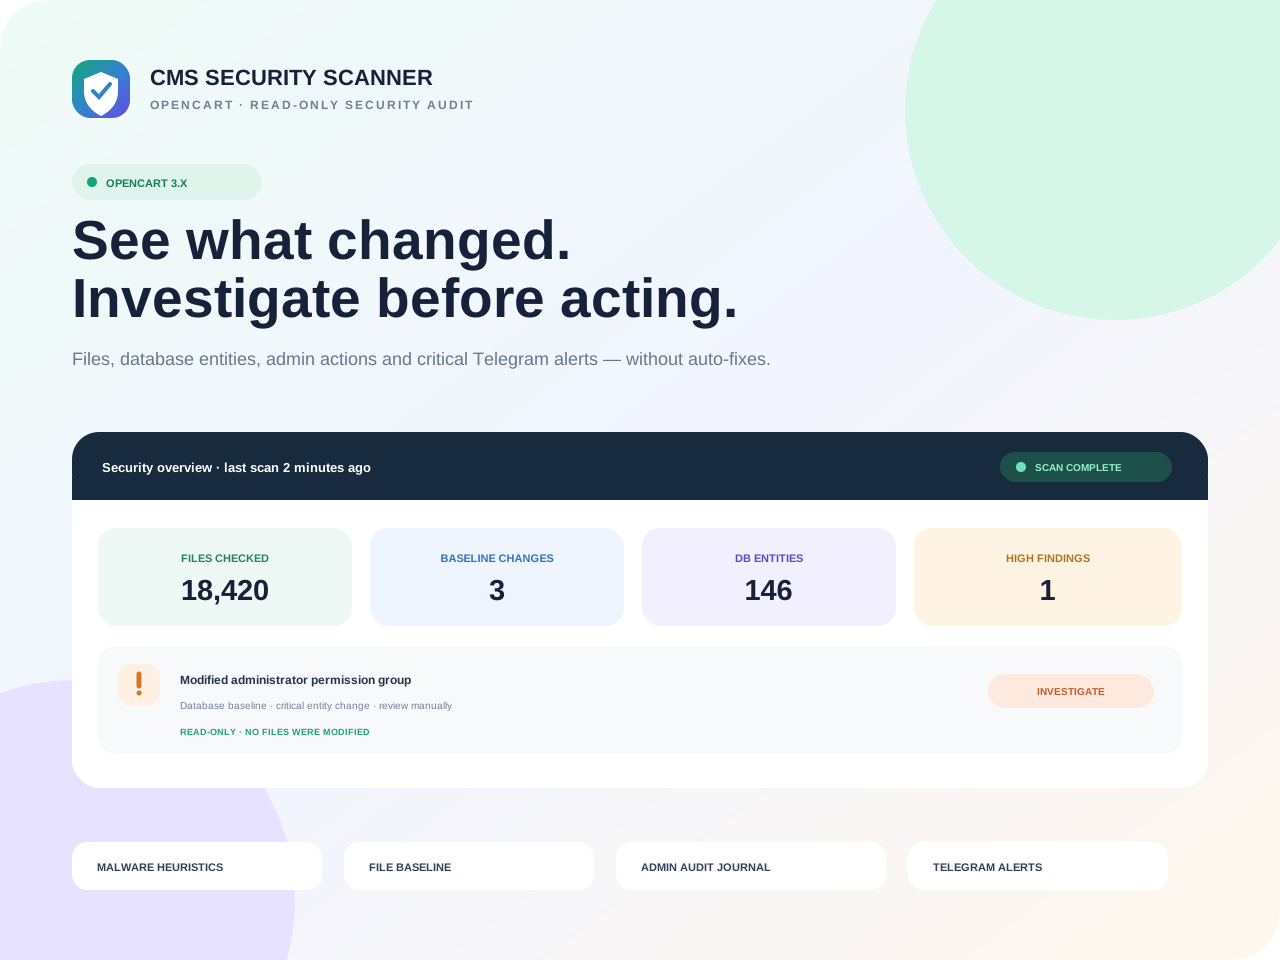
CMS Security Scanner gives a store owner a clear risk picture: malware-oriented file checks, new/changed/missing file detection, security-relevant database baselines and an audit trail of risky administrator actions.
Four security layers in one report
Filesystem, integrity baseline, database and administrative changes are reviewed together. Findings include severity and context for manual investigation.
Malware heuristics
Webshell behaviour, obfuscation, encoded payloads, PHP in non-PHP files and known denylisted hashes.
Store-specific baseline
After manual review, remember current hashes and detect files that are new, modified or missing later.
Database controls
Administrators, permissions, events, modifications, extensions, payment settings and suspicious code in editable content.
Administrator audit
Permission, administrator, extension, modification, event and payment changes are recorded in a dedicated journal.
Telegram for high risk
High and critical findings can be pushed to Telegram without waiting for the next Back Office visit.
Investigation history retained
Uninstall disables integration while preserving reports, baselines and journal data for recovery or investigation.
A safe first-run sequence
A scanner is not a substitute for incident response
A heuristic match is an investigation lead, not automatic proof of compromise. There is no CVE feed, official release-manifest comparison or php.ini remediation. Confirm a serious finding manually or escalate it to a specialist.
OpenCart / ocStore 3.x
Installs as OCMOD. Syntax is checked on PHP 5.6 and 7.4; the actual PHP version must also be supported by the installed OpenCart build.
Included with the purchase
Installation-ready ZIP, readable unencrypted source, read-only engine, file/database checks, baseline, audit journal, Telegram alerts, documentation, 12 months of updates and launch support.